Authorized Security Testing
Professional Network Port Scanning for Authorized Security Assessment
Django-powered platform for cybersecurity professionals. Scan authorized networks, identify open ports, generate detailed reports, and maintain complete audit trails—all from your local environment.
Security and Compliance First
- Server-Side Target Authorization All scan targets are validated against configurable allowlists before execution. Server-side enforcement prevents frontend bypass and ensures only authorized lab environments, development systems, and client-approved networks are assessed.
- Complete Authentication & Access Control Django's robust authentication system with session management, CSRF protection, and user isolation. Each user can only access their own targets, scans, results, and reports. Role-based permissions support team environments.
- Rate Limiting & Resource Controls Configurable limits on concurrent scans per user, maximum ports per scan, timeout ranges, and scan frequency. Server-enforced quotas prevent resource exhaustion and ensure responsible usage of scanning infrastructure.
- Comprehensive Audit Logging Detailed logging of all scan activity, authentication events, authorization decisions, and system errors. Maintain complete audit trails for compliance, security reviews, and incident investigation with timestamped records.
- Standalone Deployment Architecture No external dependencies on third-party backends, cloud services, or hosted platforms. Deploy to your own infrastructure with full control over data, security policies, and network access. Supports air-gapped environments.
- Professional Security Practices Input validation, parameterized database queries, secure password hashing, environment-based configuration, and separation of concerns. Built following Django security best practices and OWASP guidelines for web application security.
The Evolution
From Basic Scripts to Professional Security Platform
Traditional Port Scanning Challenges
- Basic Python scripts require manual execution from command line with no history or reporting capabilities.
- Sequential scanning is painfully slow when assessing large port ranges across multiple targets.
- No authentication or authorization controls mean anyone with script access can scan any target.
- Results printed to console are lost immediately with no database storage or export functionality.
- No validation of targets leads to accidental scanning of unauthorized systems and potential legal issues.
- Impossible to track scan history, compare results over time, or generate professional client reports.
PortSentinel's Professional Approach
- Complete Django web application with user authentication, role-based access control, and secure session management.
- Concurrent scanning engine with configurable worker pools scans thousands of ports in seconds instead of hours.
- Server-side target allowlisting and authorization validation ensures only approved lab and test environments are scanned.
- PostgreSQL database stores complete scan history with searchable results, filtering, and detailed audit trails.
- Input validation, rate limiting, CSRF protection, and scan quotas prevent abuse and ensure responsible usage.
- Professional PDF, CSV, and JSON reports suitable for client deliverables and security documentation.
Enterprise-Grade Scanning Features
Target Management & Authorization
Save and organize authorized targets with descriptions, network details, and authorization notes. Server-side allowlist validation prevents unauthorized scanning. Manage home labs, development environments, and client-approved test systems with complete audit trails.

Customizable Scan Profiles
Create reusable scan profiles for common assessment scenarios. Quick Scan for rapid checks of critical ports, Standard Scan for comprehensive coverage, or Custom Scan with your specific port ranges. Configure timeout, concurrency, and port lists with server-enforced safety limits.
Real-Time Scan Monitoring
Watch scans progress in real-time with live status updates, port completion tracking, and open port discovery notifications. Cancel running scans if needed. View elapsed time, estimated completion, and detailed progress metrics through polling-based dashboard updates.
Comprehensive Scan History
Access complete scan history with filtering by target, status, date range, and results. Search across thousands of historical scans. Compare results over time to identify configuration changes, track remediation progress, and maintain detailed security assessment records.

Professional Report Generation
Generate client-ready reports in PDF, CSV, or JSON formats. PDF reports include executive summaries, detailed findings, scan configuration, and professional formatting suitable for security documentation. Export raw data for integration with other security tools and workflows.
Security Dashboard & Analytics
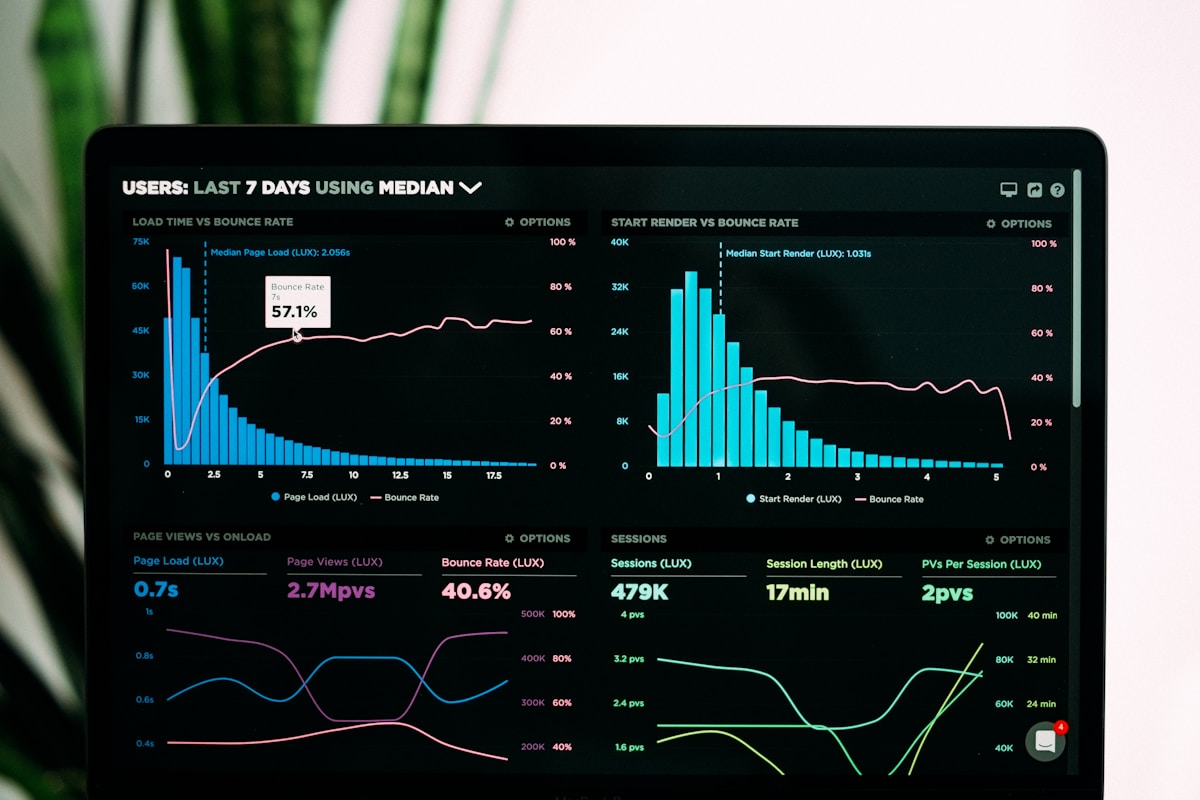
Visualize scan activity, track open port trends, and monitor assessment statistics. View most commonly discovered open ports, scan success rates, and historical activity patterns. Dashboard provides actionable insights for security posture improvement.
Complete Security Assessment Toolkit
Built on Django's robust framework with PostgreSQL database support, complete authentication system, and Django ORM for reliable data management. Run locally on Windows, Linux, or Mac, or deploy to your own VPS with full control over your scanning infrastructure.
Refactored from basic socket scanning to a professional concurrent scanning engine with ThreadPoolExecutor support, configurable timeouts, intelligent error handling, and structured result output. Scan thousands of ports efficiently while maintaining system stability.
Celery and Redis integration enables non-blocking scan execution with real-time progress tracking. Launch comprehensive scans without tying up your web interface, monitor multiple concurrent assessments, and receive notifications when scans complete.

Simple, Secure Scanning Workflow
-
01
1. Add Authorized Targets
Register your authorized lab environments, development servers, or client-approved test systems. Provide target details, authorization notes, and network information. Server-side validation ensures targets meet allowlist requirements before any scanning occurs.
-
02
2. Configure Your Scan
Select a target and choose a scan profile or customize your assessment parameters. Define port ranges, set timeout values, and configure concurrency levels. All settings are validated server-side against safety limits to prevent resource exhaustion and ensure responsible scanning.
-
03
3. Launch Background Scan
Submit your scan to the Celery task queue for background processing. The Python scanner engine executes concurrently using ThreadPoolExecutor while you continue working. Monitor real-time progress through the dashboard with live status updates and port discovery notifications.
-
04
4. Analyze Results & Generate Reports
Review detailed scan results with sortable, filterable port listings. Identify open ports, analyze service exposure, and compare against previous assessments. Generate professional PDF reports for documentation or export raw data in CSV/JSON for integration with your security workflow.
Built for Performance and Security
What Security Professionals Say
The Django architecture gives us complete control. We run PortSentinel on our own infrastructure, customize scan profiles for client needs, and generate reports that look professional enough for executive presentations.
Moving from command-line scripts to PortSentinel was transformative. Background scanning means I can launch comprehensive assessments and move on to other tasks. The scan history and comparison features are invaluable for tracking remediation.
The authorization controls and target allowlisting give me confidence we're only scanning approved systems. The audit trail and detailed logging are essential for our compliance requirements and client documentation.
Trusted by Security Professionals
PortSentinel transformed our security assessment workflow. The Django-powered architecture gives us complete control over our scanning infrastructure while maintaining the professional reporting our clients expect.
Deploy Your Professional Security Assessment Platform
PortSentinel is a complete Django-powered network scanning solution designed for security professionals conducting authorized assessments. Download the source code, deploy to your own infrastructure, and start running professional security scans with comprehensive reporting and audit capabilities.